Your database is open to anyone
When row-level security is left off, a single crafted request returns every row your users have created, with no need to break in
For software built with AI
 Official partner
We check whether your app is as safe as it looks
You built a working product with AI and no engineering team. We check it for security vulnerabilities, exposed data and failures under real traffic, and tell you whether it is ready to launch. You get a prioritized fix plan: we make the fixes, or your own developer or AI tool can.
Common vulnerabilities
These are the issues we find most often in apps built quickly with AI, and none of them appear while you click through your own product
When row-level security is left off, a single crafted request returns every row your users have created, with no need to break in
API keys and service secrets are shipped to the client, where anyone who opens the browser's developer tools can read and reuse them
Authentication confirms who a user is but never checks what they are allowed to access, so changing an ID in the URL opens someone else's account
Each AI-generated change can loosen a rule that an earlier change locked down, and because nothing throws an error, the app gradually stops matching what you asked for
The audit checks for each of these in your code and database configuration
The problem
Shipping software you cannot inspect leaves you without the information you need to judge whether it is safe to grow. The comparison below shows what is missing and what the audit supplies.
What you can check yourself
What you know after the audit
The audit closes the gap between these columns
What we check
Each area is reviewed by a person who has seen it fail before, so nothing is left to an automated checklist alone
What a stranger can extract from your database using nothing more than a browser
What was shipped to the browser, what is stored in your repository, and what should have stayed on the server
Who can sign in, who can act as another user, and which routes never check permissions
Where the build diverged from what you asked for, such as a rule that was dropped 3 prompts ago
The queries, limits and background jobs that work for 1 user and fail at 1,000
Payments, uploads, refunds and edge cases: the flows nobody has run more than once, where a silent failure looks like success
Deliverables
Everything is written in plain language, so you can read it yourself and present it to a board, a customer or an investor without translation
Every issue is ranked by its likely cost to your business, and the report states openly what we are not yet sure of
What to fix first, what can wait and what we would leave alone. The plan is yours to keep, whoever carries out the work.
An exact total based on the number of changes and the cost per change, which you approve before any work starts
Once the fixes are in place, you receive a verification summary that a customer, partner or investor can read and rely on
Illustrative example. Your report is built from your app.
Pricing
The only decision to make now is the audit. Everything after it is priced from what the audit finds, and you approve that price before work begins.
Step 1 · Start here
$1,000one-time, fixed
Find out where your app stands and what it will cost to make it secure and stable
Step 2 · The fix
$295/ verified change
We fix what the audit found and harden your app for real traffic
Priced from your audit findings, never estimated without one
Step 3 · Stay solid
$300–600/ month
Ongoing review that keeps your app secure while you keep building with AI
Prices in US dollars.
We review every significant change and do not monitor in real time. The audit and fixes secure your app, and this layer keeps it secure while you keep building.
Process
You keep building, and we give you an independent assessment of what has been built at each stage
We check how your data is protected, who can access what, where the build drifted, and which parts will break as usage grows
What is sound, what is at risk and what we are not yet sure of, written so you can present it to your board or investors
As you keep building, we review each significant change and catch new issues before they reach production
Proof
Some of these projects were audits of apps written by other teams. We built the rest ourselves, and each one went through the same review before launch.
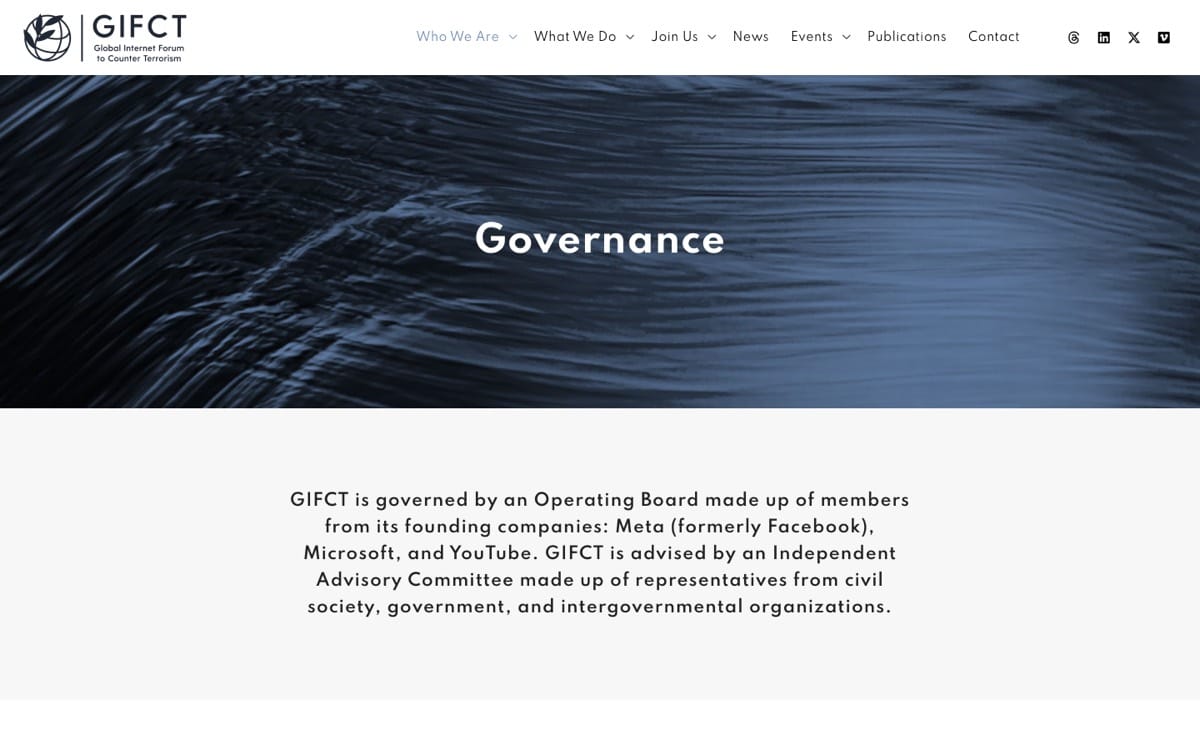
The Global Internet Forum to Counter Terrorism, founded by Meta, Microsoft and YouTube, needed one place for its Operating Board and Independent Advisory Committee to work. We built the governance portal and took it from build to launch.
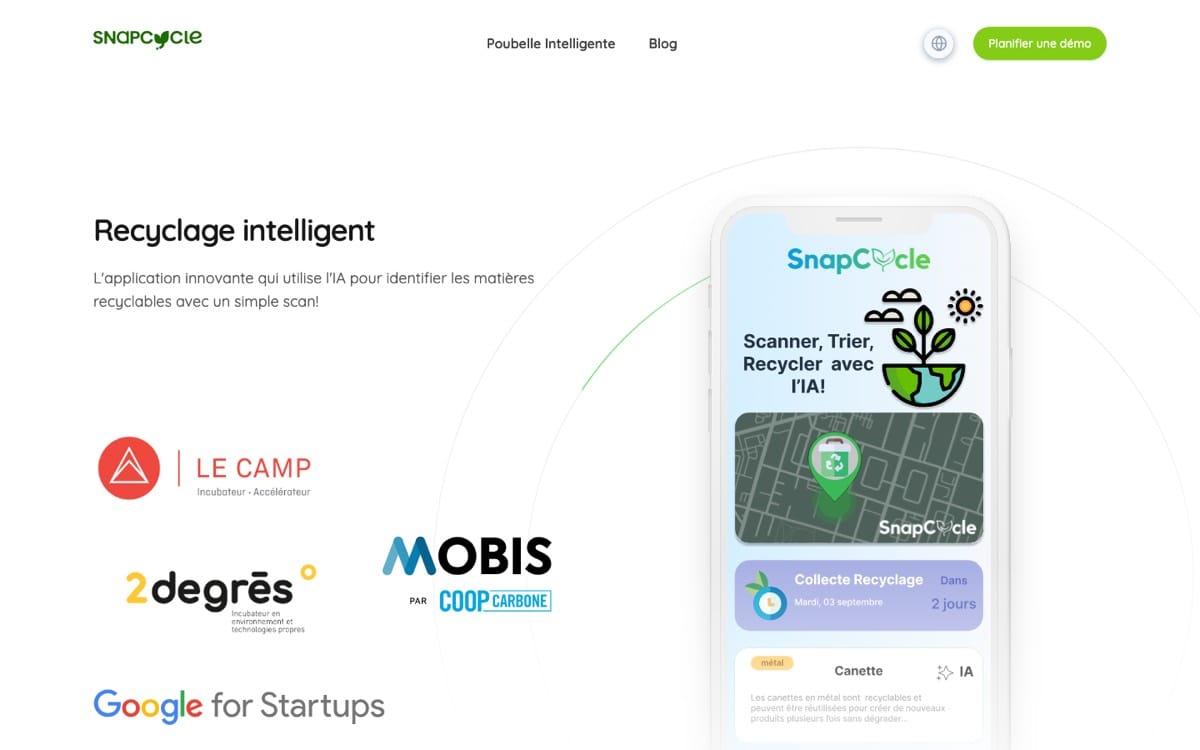
An app that identifies recyclable materials from a single scan, heading for both app stores. We accompanied the team through their technology choices and architectural decisions, the calls that are expensive to reverse later.
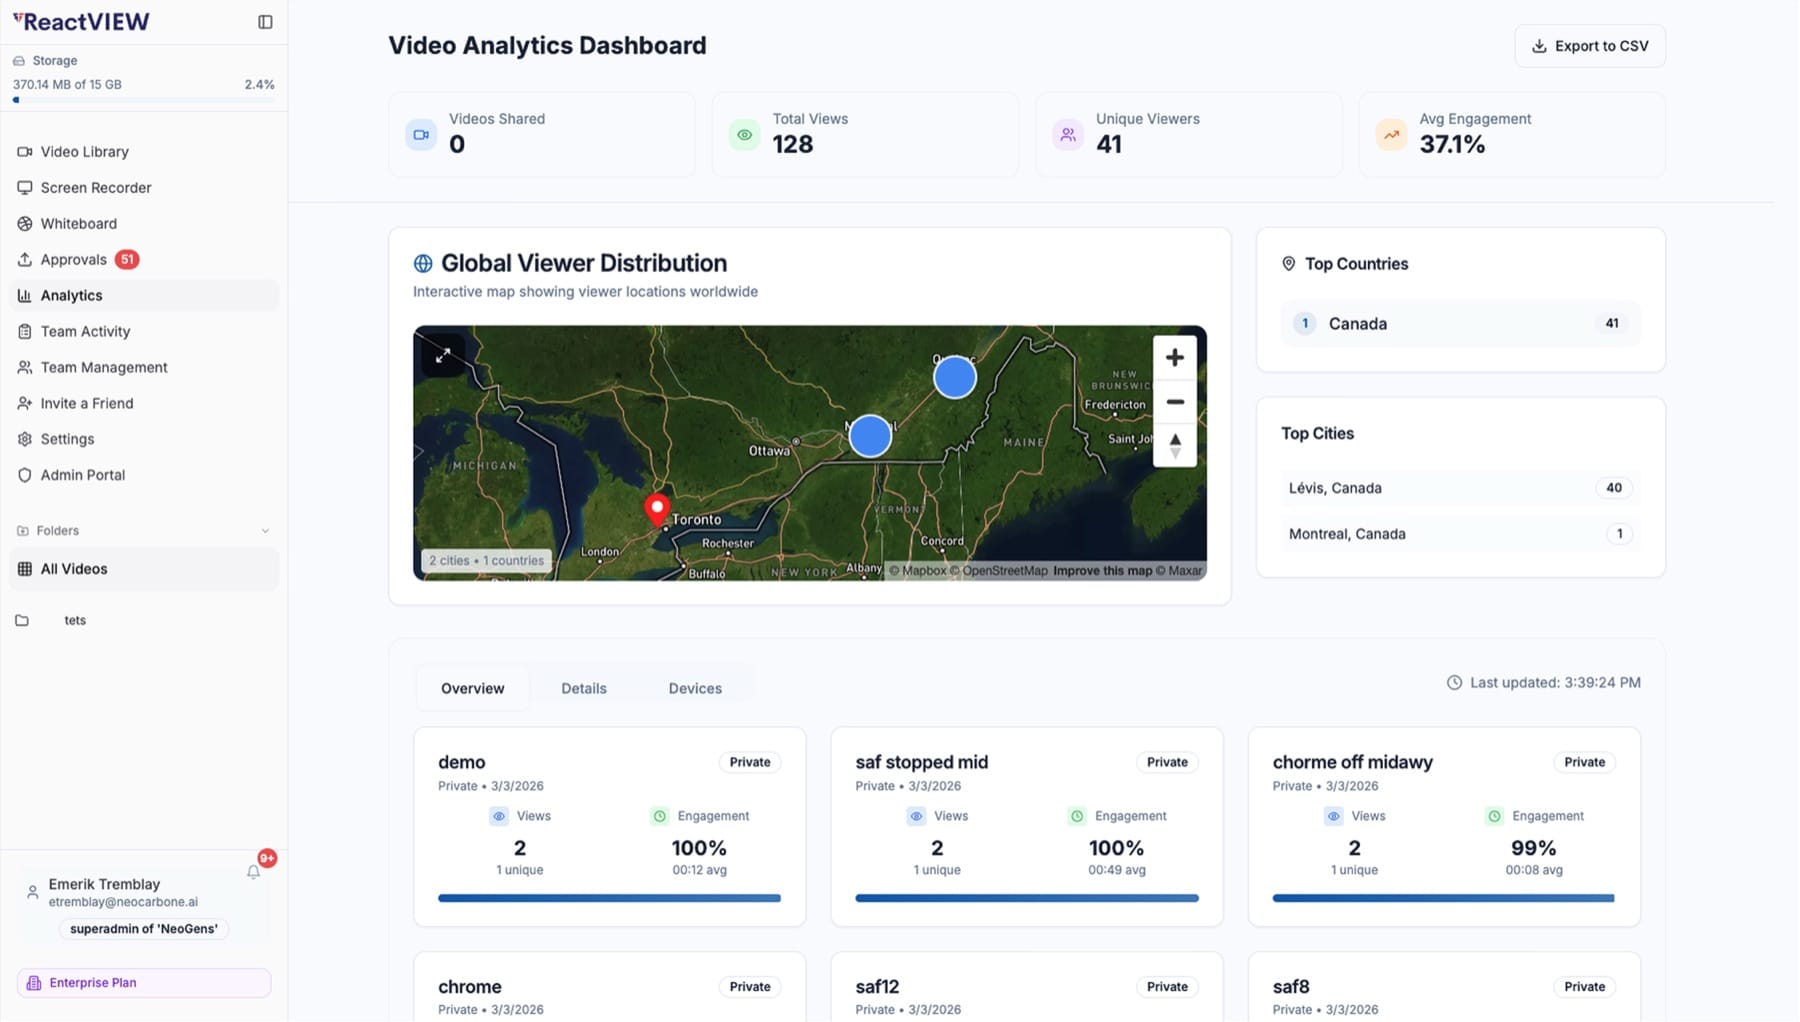
Coaches record a game, review it frame by frame, draw the play on a live tactics board, and see who watched. We joined mid-project and took over product development.
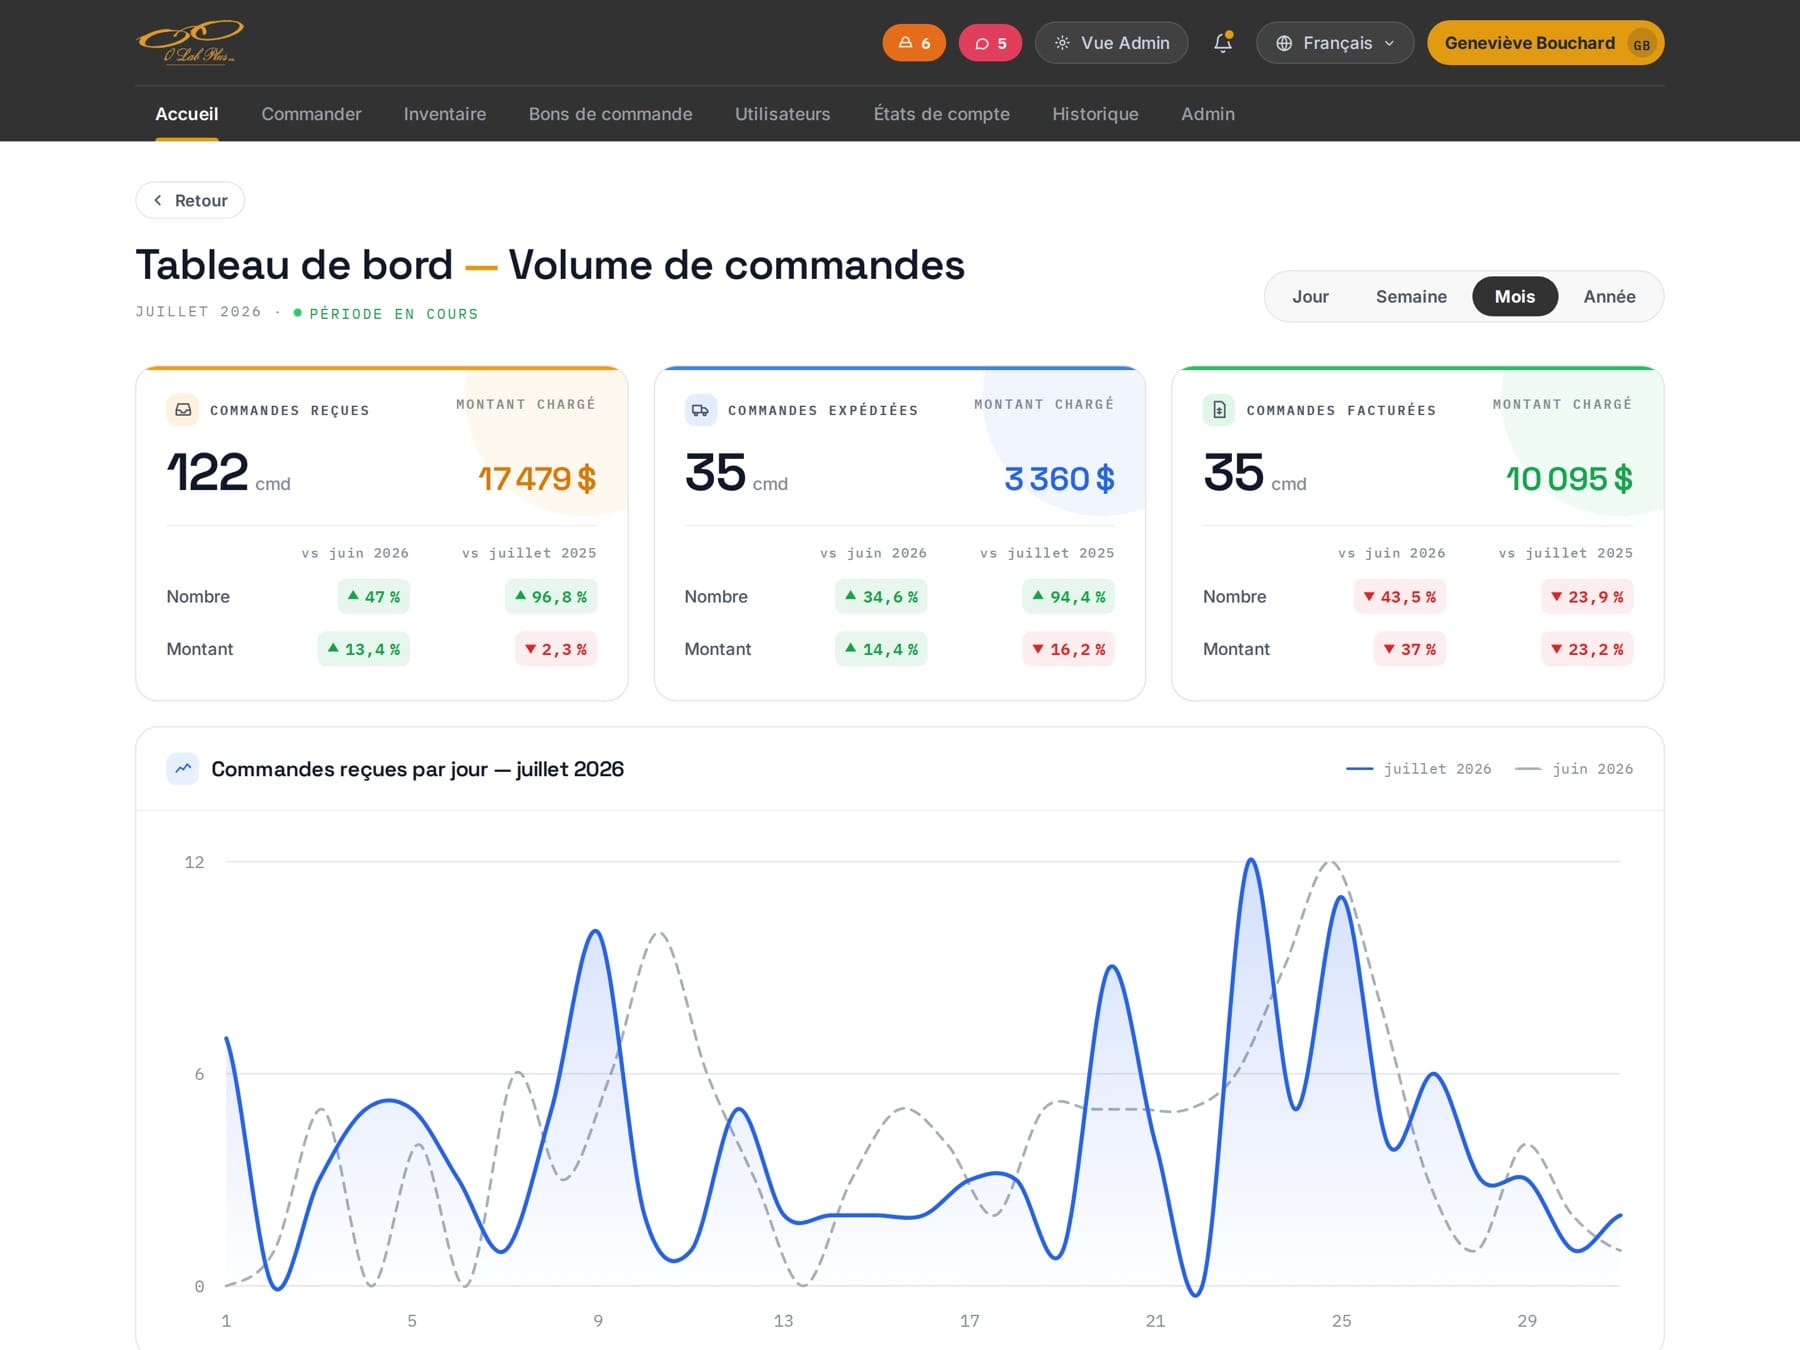
An independent optical laboratory in Brossard, Québec, serving eyecare clinics since 1987. We develop and maintain the platform, and have increased the speed and quality of each release.
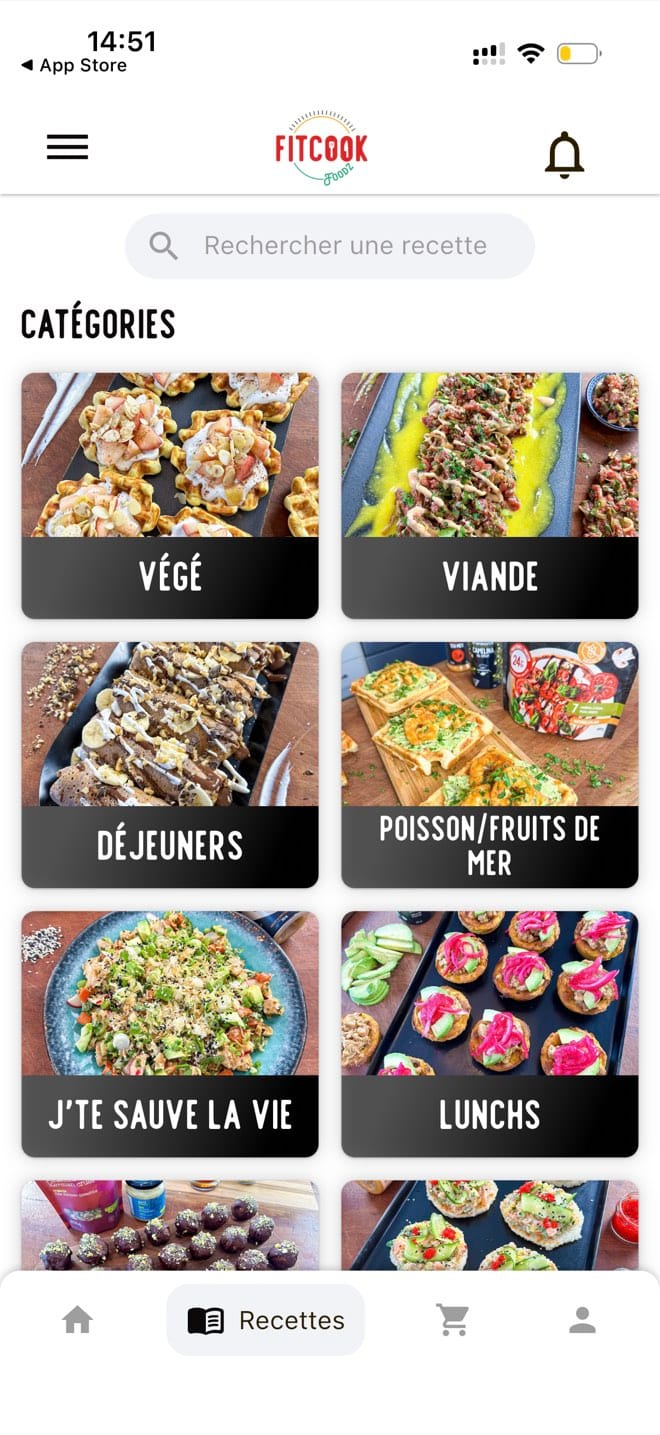


A recipe library with full nutrition data, a store integrated with Shopify, a premium subscription, cooking courses and a community feed. Live on the App Store and Google Play.
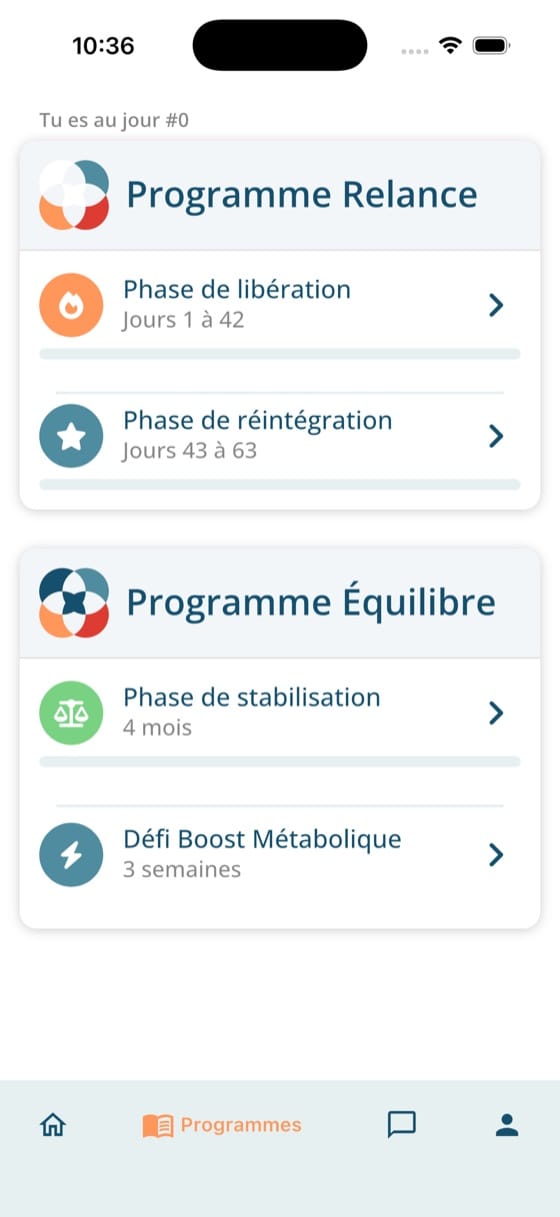
A Québec coaching program on one app the client owns: the full curriculum, a coaching messenger with voice notes and scheduled broadcasts, and every client's progress in one database
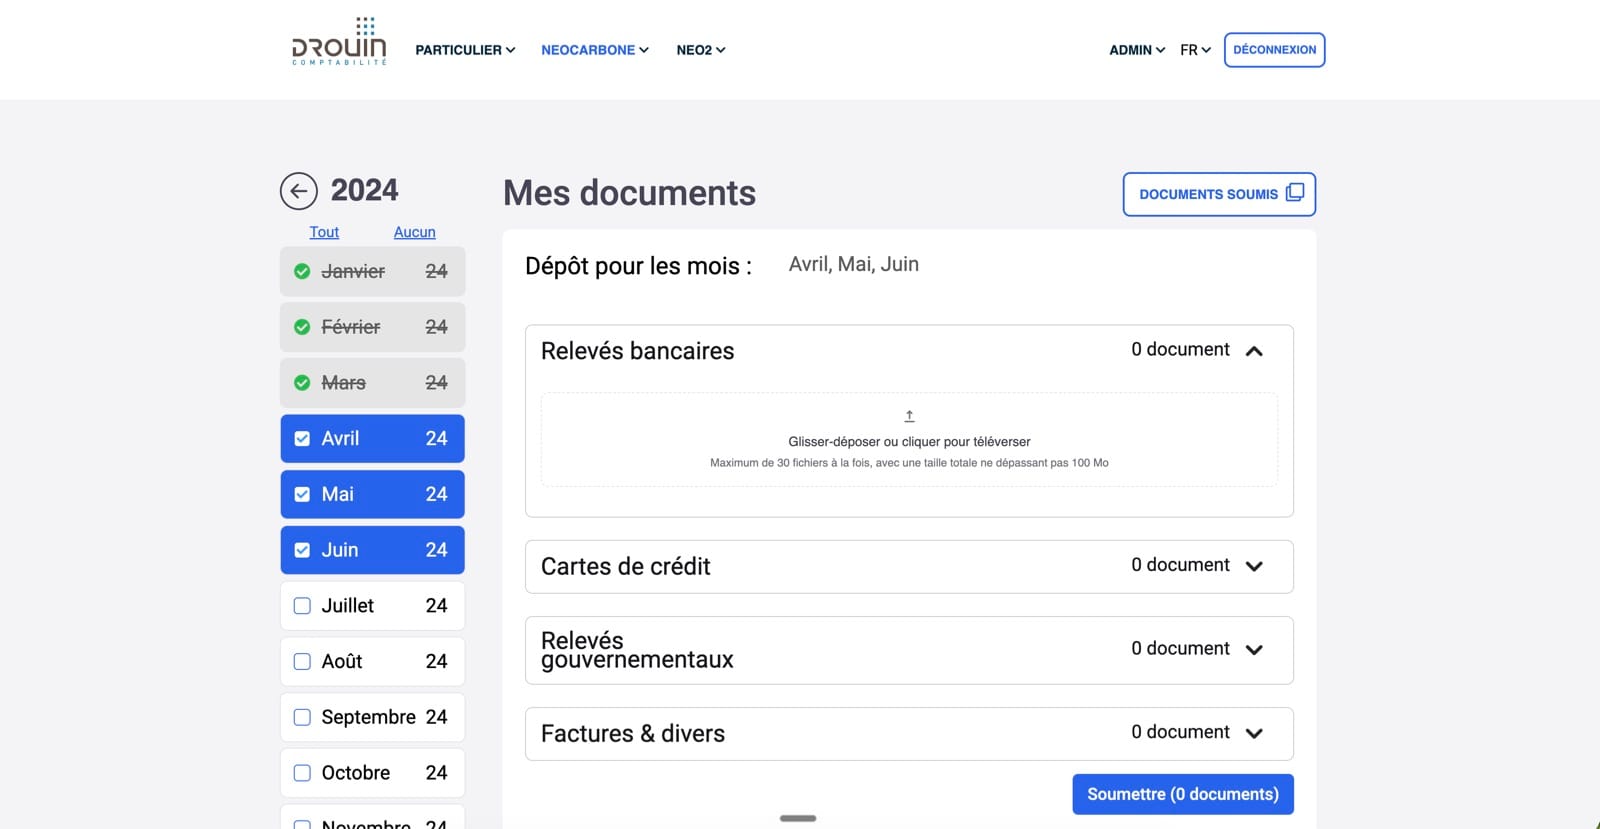
Each year, 2 Québec accounting firms collect the same tax file from every client. We built the portal that requests the documents, walks the client through the questionnaire, and sends the reminders.
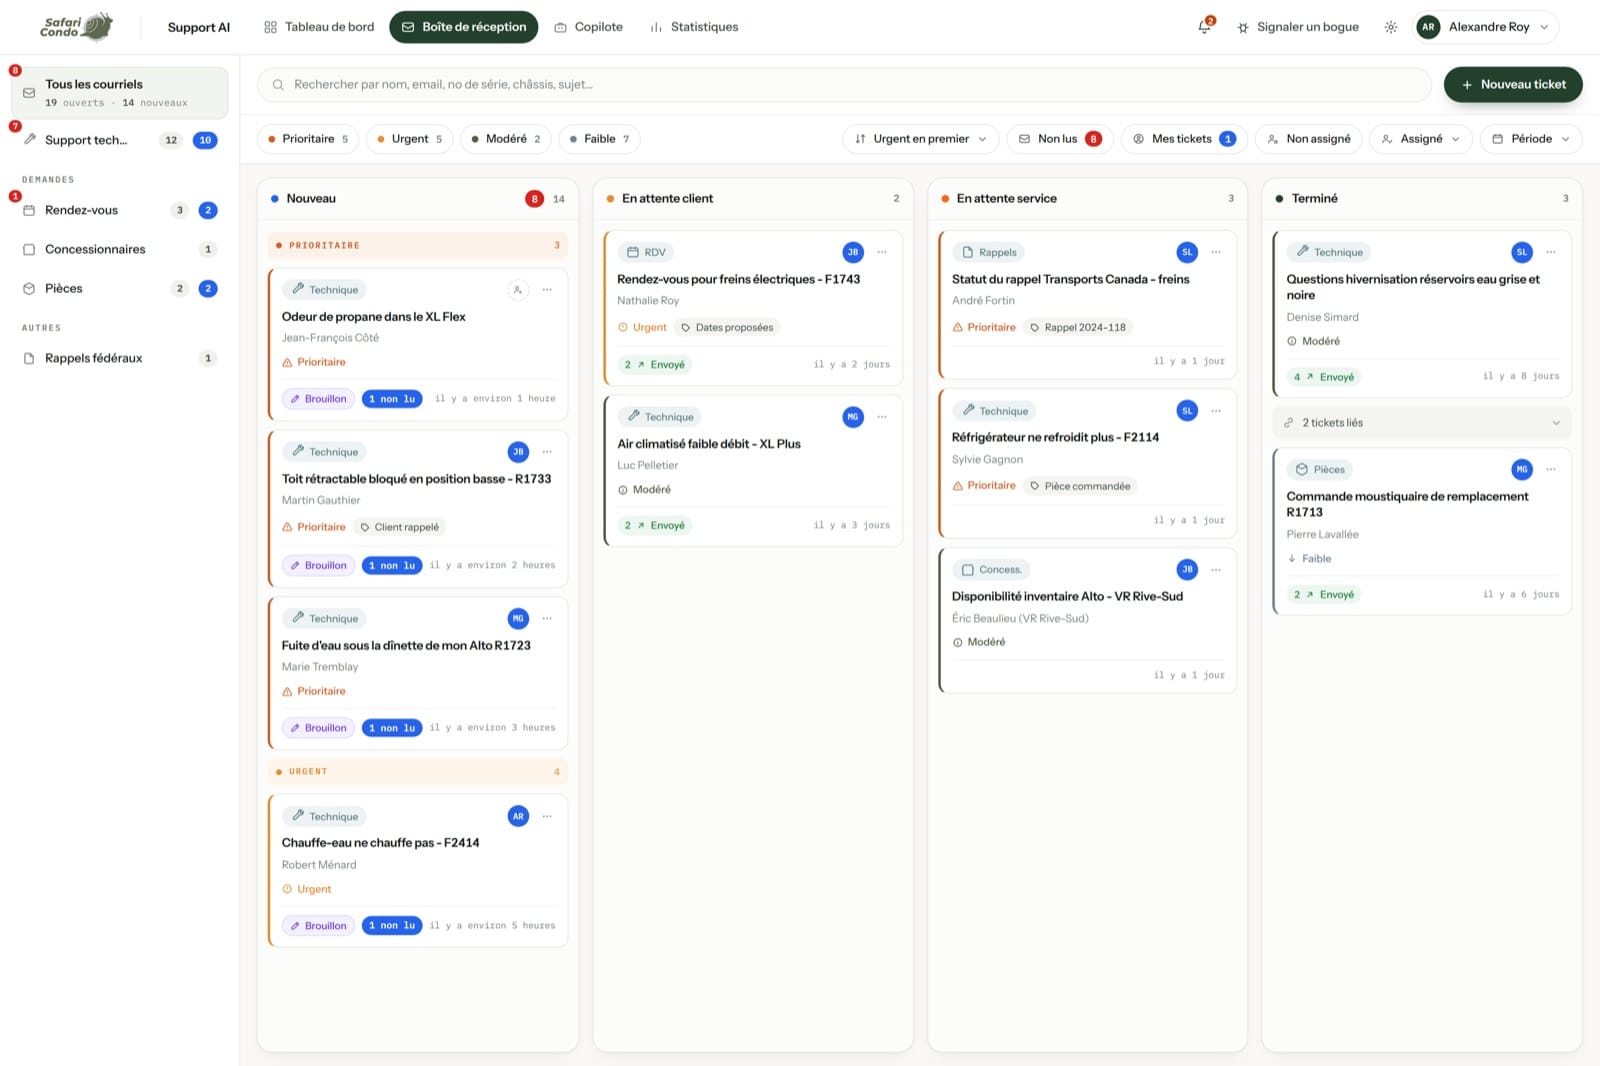
A Québec motorhome maker receiving more support requests than its team could read. We automated the support desk, so every request is categorized and arrives with a drafted reply and the relevant documentation attached.
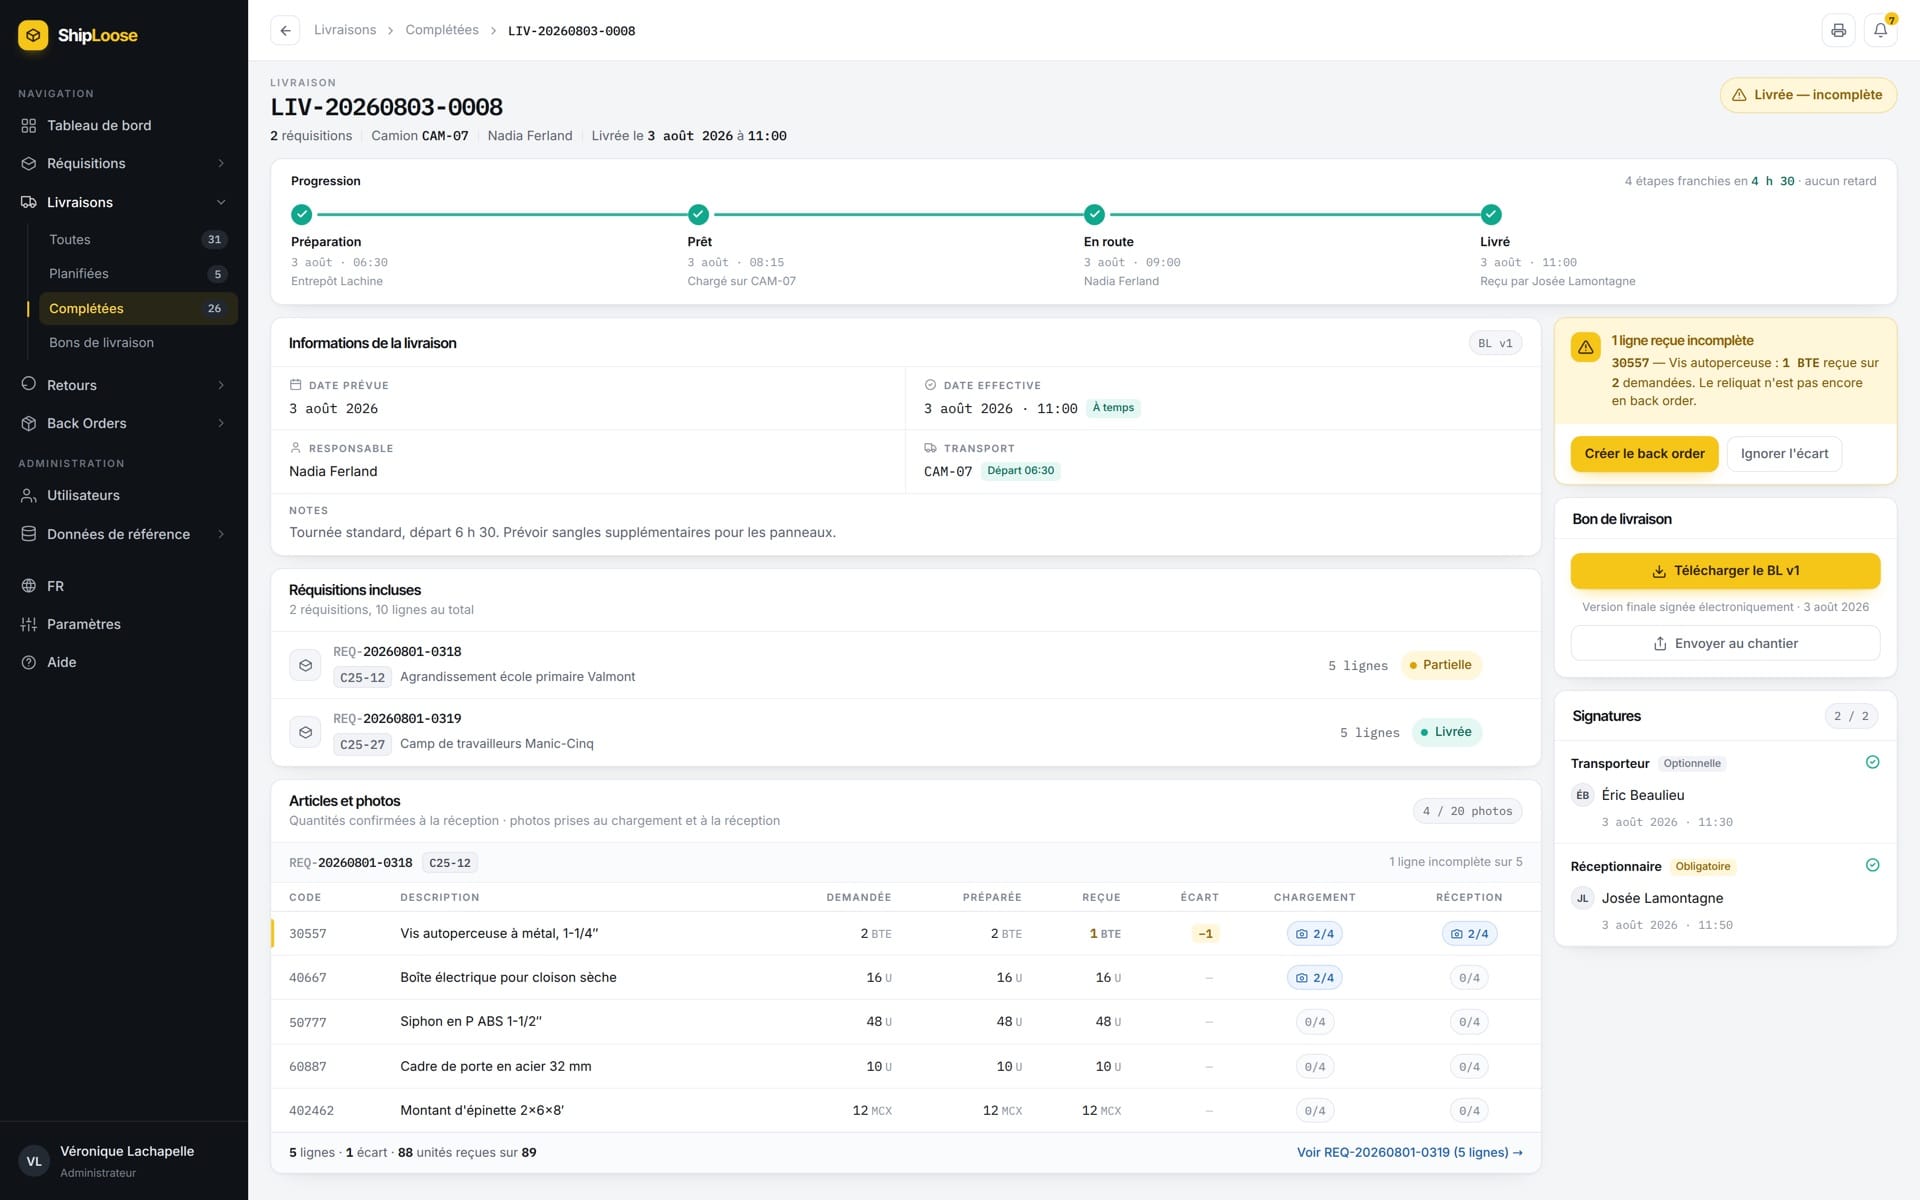
A modular construction manufacturer moved every material request between its sites and its warehouse through one shared spreadsheet. We scoped the replacement, then built the application that took its place.
Read the case studyWhere this is going
Today, we secure one app at a time and keep it secure as it changes. Our longer-term goal is coherence everywhere, where the people, policies, processes and AI in an organization stay consistent with each other.
We start with a single app because that is where the need is most urgent today, and we are building toward whole organizations that stay consistent with what they intend to do
Now
An audit of what is broken, exposed or drifted from what you meant, reviewed by a person and written in plain language
Next
A layer that keeps checking your app against what you meant while you change it, so the findings stay current after the report is delivered
The horizon
People, policies, processes and AI kept consistent with each other across a whole organization, beyond a single app
This describes where we are heading, not services we offer today
FAQ
Yes. The audit is designed for founders who are not technical. We work inside the tools you already use and are an official Lovable partner, so you will not need to explain your architecture or bring an engineer to read the report.
No. The audit is read-only, so we do not change anything in your app. If you go ahead with fixes, you approve the scope of every change first, and we verify each one before it ships.
Then you receive that conclusion in writing, and it is the deliverable: documented confirmation that your app is sound, which is a useful result in its own right
No. The findings report and the fix plan are yours to give to your own developer, another studio or your AI tool. We would welcome the work, but the audit is a complete deliverable on its own.
A scanner matches known patterns. We check whether your app does what you meant: that the data is locked down, the access rules are consistent and the app holds up under real users. We also state what we are not sure of, which a scanner cannot do.
$295 per verified change. Your audit sets the number of changes, typically 6 to 10 for a small app, and you receive an exact total to approve before any work starts. Prices in US dollars.
Next step
The audit gives you a plain-language account of your app's security and a priced plan for everything it needs fixed
Pricing
The only decision to make now is the audit. Everything after it is priced from what the audit finds, and you approve that price before work begins.
Step 1 · Start here
$1,000one-time, fixed
Find out where your app stands and what it will cost to make it secure and stable
Step 2 · The fix
$295/ verified change
We fix what the audit found and harden your app for real traffic
Priced from your audit findings, never estimated without one
Step 3 · Stay solid
$300–600/ month
Ongoing review that keeps your app secure while you keep building with AI
Prices in US dollars.
We review every significant change and do not monitor in real time. The audit and fixes secure your app, and this layer keeps it secure while you keep building.